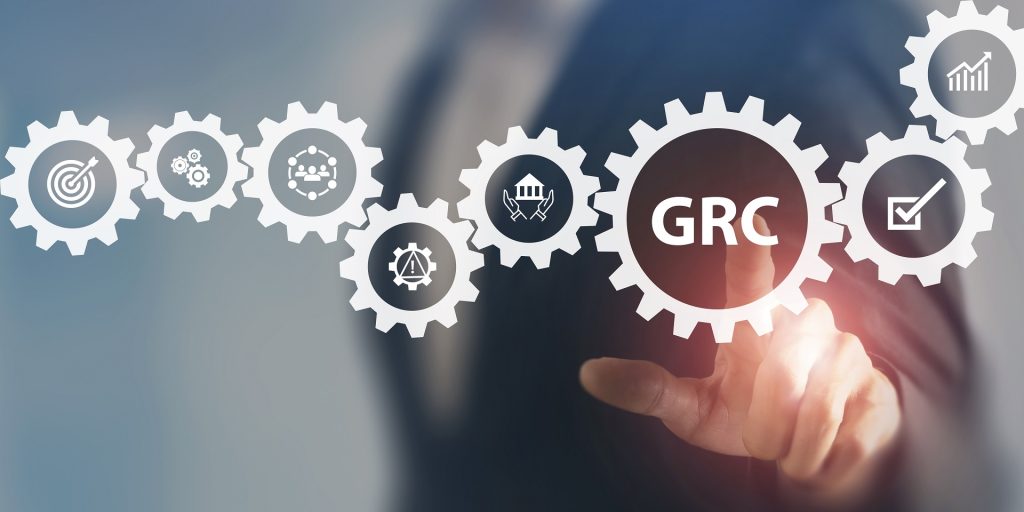
In today’s fast-paced and complex business environment, Governance, Risk, and Compliance (GRC) is more than a regulatory requirement — it’s a strategic asset. By embedding GRC practices into everyday operations, organisations can strengthen decision-making, build resilience, and uncover growth opportunities.

1. The GRC Trifecta: Governance, Risk, and Compliance
- Understanding the interconnected nature of governance, risk management, and compliance.
- Common challenges include fragmented frameworks, reactive compliance, and outdated risk registers.
2. Benefits of a Unified GRC Strategy
- Integration of governance frameworks, risk registers, and compliance monitoring enhances agility and efficiency.
- Real-world examples show how strong GRC alignment reduces costs, improves transparency, and increases stakeholder trust.
3. Implementing Best Practices
- Align corporate strategy with regulatory obligations to maintain compliance without compromising growth.
- Build dynamic risk registers and formalise risk management policies that adapt to change.
4. The Role of Technology in GRC
- Risk and compliance software enhances real-time monitoring, reporting, and risk intelligence.
- Data-driven insights empower leadership to anticipate risks and adjust faster.
Conclusion
GRC done right is a driver of transformation, not just a control function. It helps businesses stay focused, aligned, and future-ready. NSS is here to help you build a GRC model that fits your operations and supports confident, compliant growth.